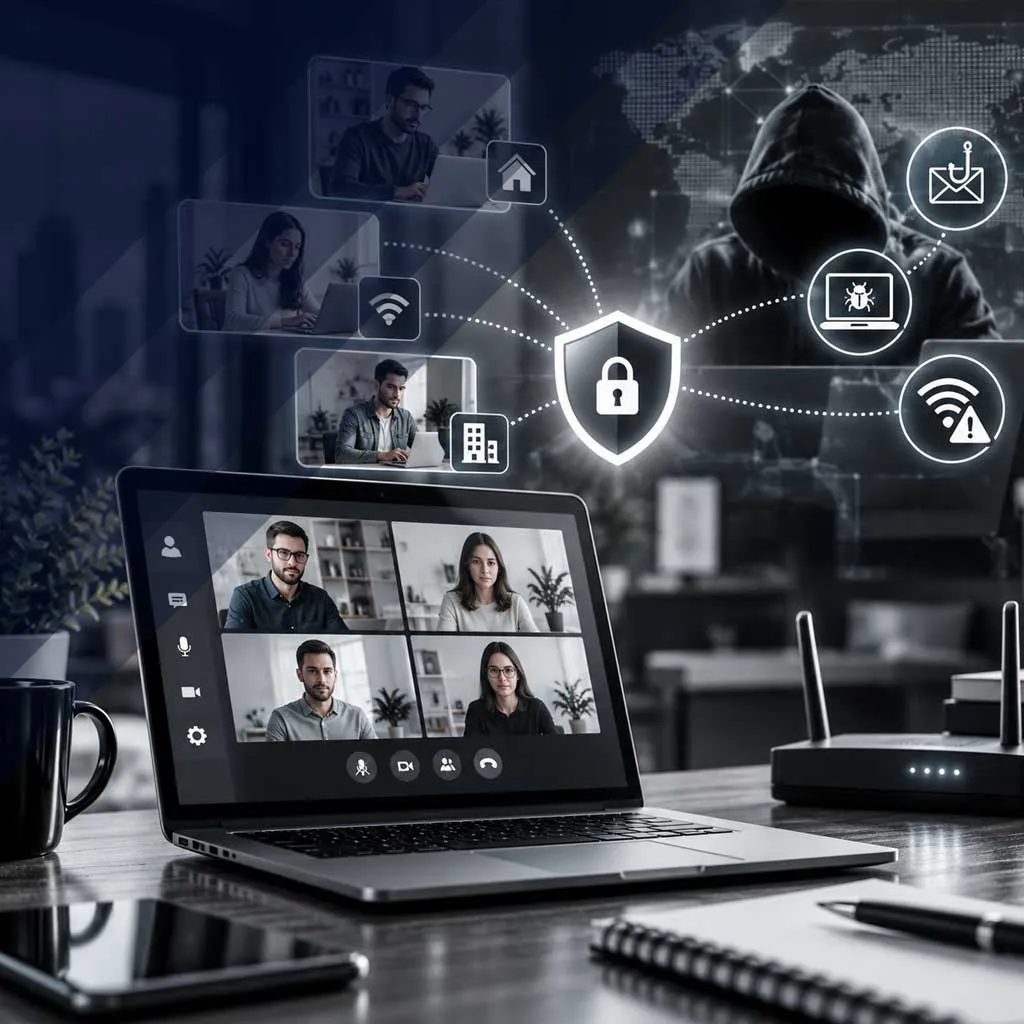
Hybrid working is now normal for most Dartford businesses. Staff split their week between the office, home and the occasional coffee shop, and that flexibility is good for everyone. The catch is that every location outside the office is a place your usual protections may not reach.
Attackers know this. Rather than trying to break through a well defended office network, they go after the person working from the kitchen table. Here are the three routes we see most often, and what you can do about each.
1. Phishing that looks like everyday work
Remote staff rely heavily on email and Teams messages, so a convincing fake fits right in. A message that appears to come from a manager, a supplier or Microsoft asks the reader to open a document, approve a payment or “confirm” their password.
Without a colleague nearby to sanity check a strange request, people are more likely to click.
How to stop it
- Turn on multi-factor authentication (MFA) for Microsoft 365 and every other business system, so a stolen password alone is not enough
- Use advanced email filtering to block spoofed senders and dangerous links before they reach inboxes
- Run short, regular cyber security awareness training so staff recognise the warning signs
- Agree a simple rule: any request to change bank details or make an urgent payment is checked by phone
2. Unsafe home and public Wi-Fi
Home routers often still use the default password printed on the back, and many have not had a firmware update in years. Public Wi-Fi in cafes, hotels and stations can be even riskier, as anyone on the same network may be able to watch unencrypted traffic or set up a fake hotspot with a convincing name.
How to stop it
- Ask staff to change default router passwords and keep router firmware updated
- Provide a business VPN or secure access service for connecting to company systems
- Encourage staff to use their phone’s hotspot rather than public Wi-Fi for work
- Make sure business apps only work over encrypted connections
3. Laptops that fall behind on updates
A laptop that rarely connects to the office network can quietly miss weeks of security updates. Each missed patch is a known weakness that attackers can scan for automatically. Personal devices used for work are even harder to keep track of.
How to stop it
- Manage every business device centrally, for example with Microsoft Intune, so updates are pushed wherever the laptop is
- Install endpoint detection and response to spot and stop suspicious activity in real time
- Encrypt laptop drives so a lost or stolen device does not mean lost data
- Set a clear policy on whether personal devices can access company data, and on what terms
Bringing it together
None of these fixes are expensive or complicated on their own. The challenge for small businesses is making sure they are all in place, on every device, for every member of staff, and that they stay that way.
That is where a managed approach helps. We look after security for remote and hybrid teams across Dartford and north Kent, from MFA and email filtering to device management and staff training. If you are not sure how well protected your home workers really are, get in touch and we will take a look.